Security & Governance
Articles about Security & Governance, with practical notes on executable business ontologies, governed data, application development, and agent workflows.
-
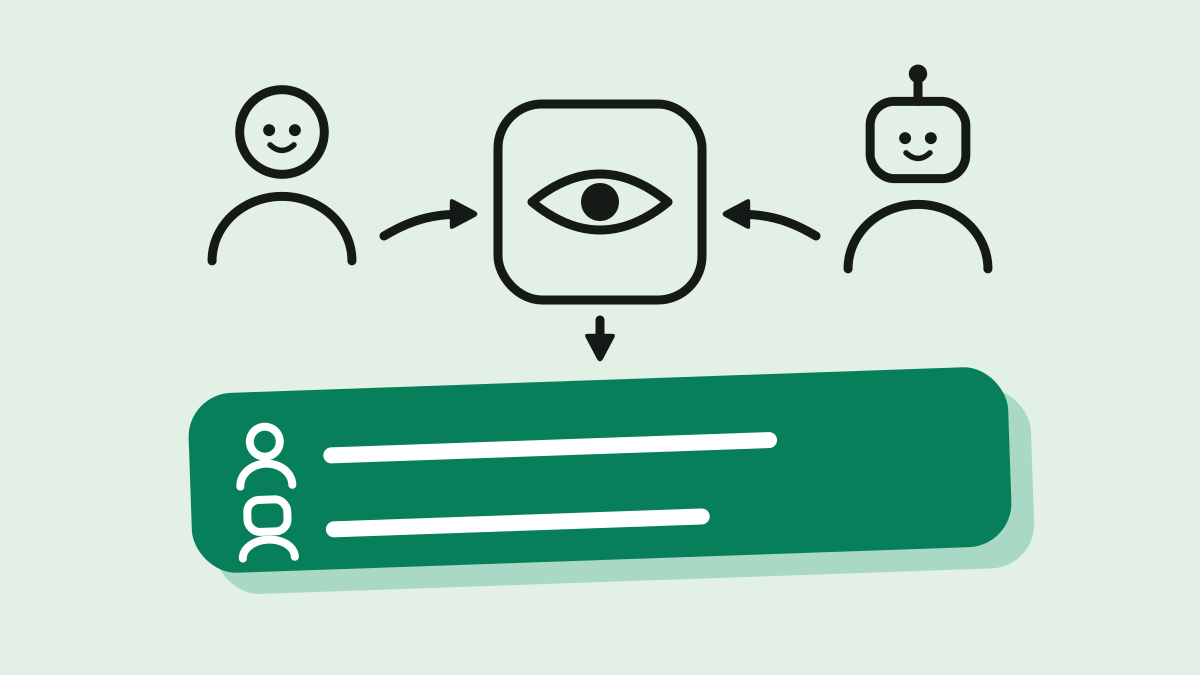
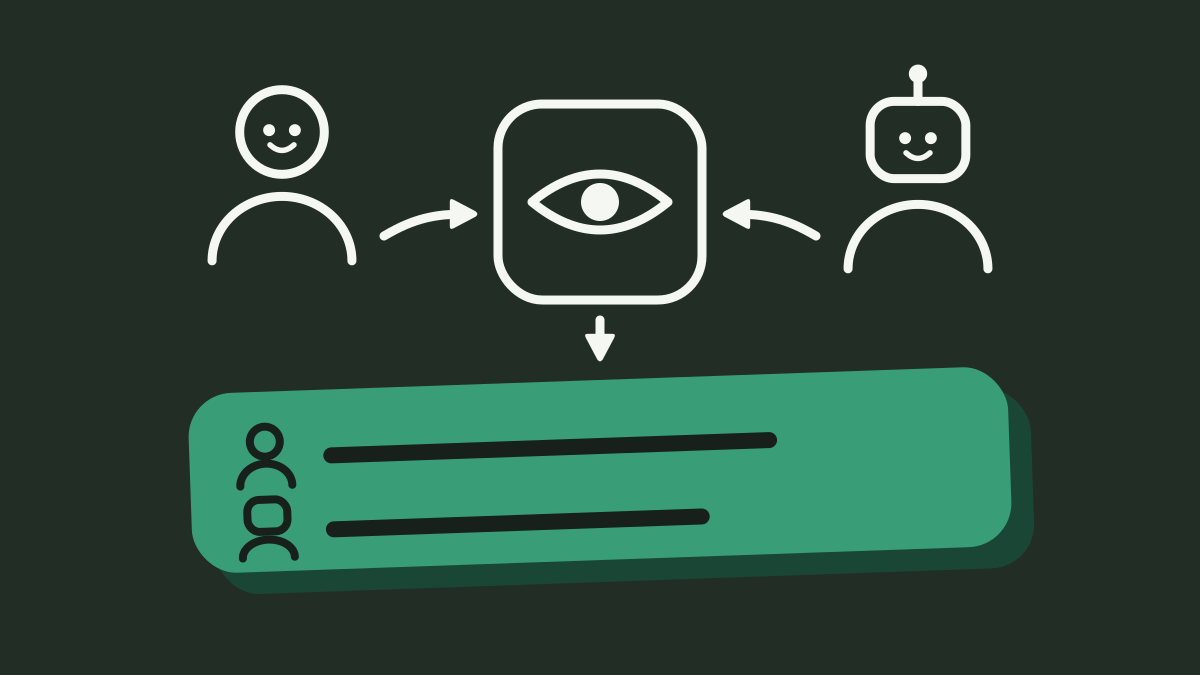
Can You Prove Who Opened a Customer Record, Including an AI Agent? Record-View Auditing, and the Four Things a View Row Never Records
On @objectstack/cli 18.3.0, a person's REST read and an agent's MCP get_record each left one read row in sys_audit_log; a list, an unlisted object and a refused read left none. What a row holds, and the four things it never does.
Security & Governance IT Leaders Audit trailRecord-view auditingAI agentsCompliance -
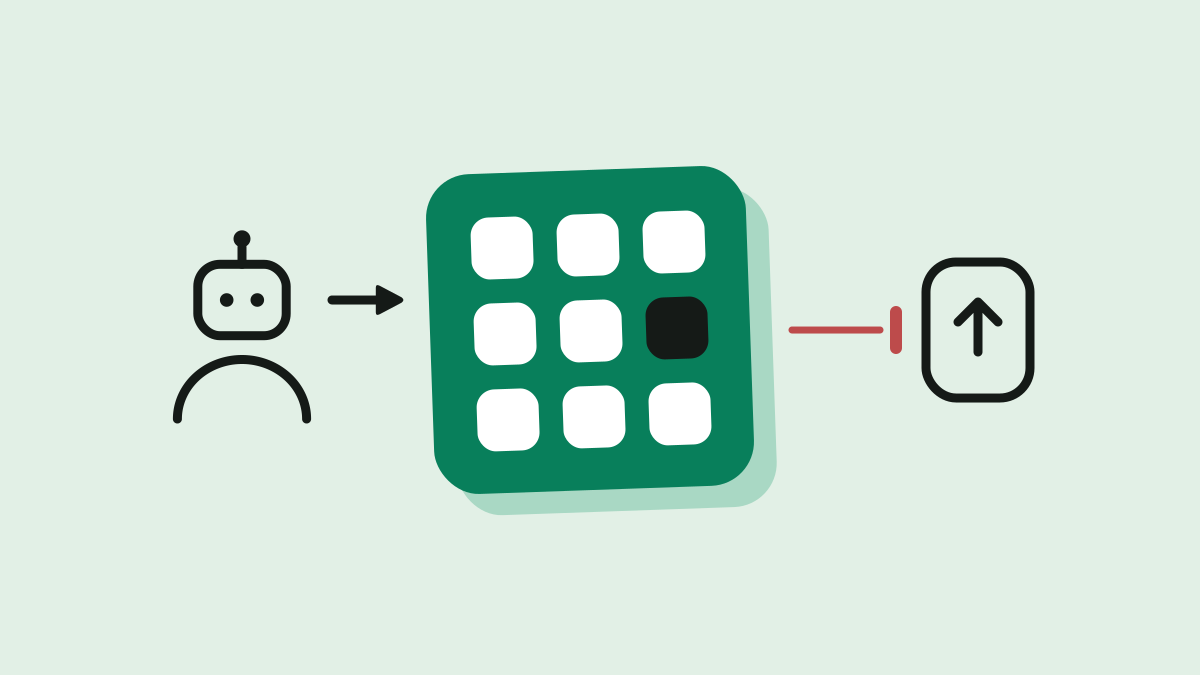
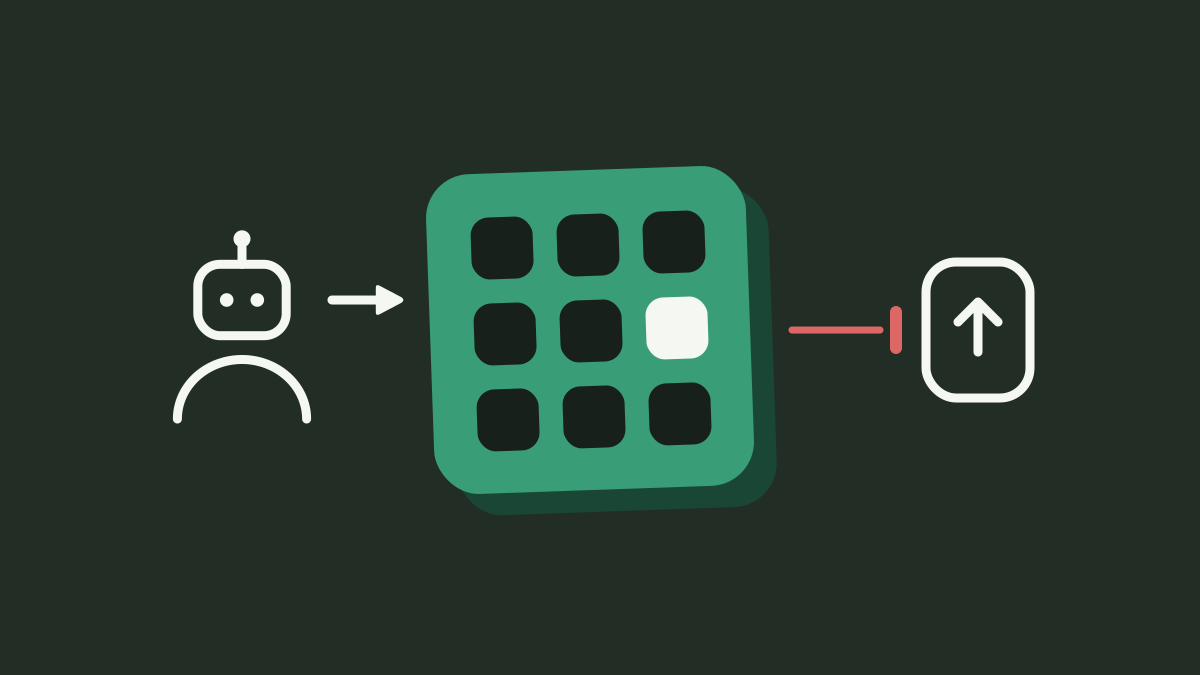
How Do You Catch an AI's Silent Permission Change Before It Ships? The Access-Matrix Snapshot Gate, on a 7-Entry CRM
On @objectstack/cli 18.2.0, os validate passes an agent's allowDelete false-to-true flip with no finding. os compile on an opted-in app fails the build with one line naming who gains what, until a human regenerates the snapshot.
Security & Governance Developers AI agentsAgent permissionsReviewable diff -
How to Self-Host an AI App Platform: ObjectStack from Install to Verified
A walkthrough of self-hosting the open-source ObjectStack runtime: the compiled-artifact model, the database driver everyone misses, how to prove the install is correct, and what you are now on call for.
Security & Governance IT Leaders -
Power Platform Lock-In: Dataverse, Azure, and the Self-Host Tradeoff
Power Platform is already inside the Microsoft tenant, but self-hosting, Dataverse export, AI usage pricing, and sovereignty requirements matter for long-running systems.
Security & Governance IT Leaders DataversePower AppsPower Platform -
Is Lovable Safe for Production? The Access-Control Review Problem
Lovable can turn a sentence into a full-stack app, but production data depends on access control the accountable builder must be able to inspect, understand, and approve.
Security & Governance Developers Lovable -
Open vs. Closed Enterprise Ontologies: Who Owns the Business Definition Layer?
Five platforms shipped a business definition layer between Nov 2025 and Aug 2026 — two as an ontology, three as a semantic layer — and most opened an MCP read path, not the definition. Protocol-open, definition-closed.
Security & Governance Business Leaders OntologySemantic layerMCPFabric IQUnity CatalogSnowflakePalantirLooker -
EU AI Act Audit Readiness: Can Your AI Runtime Produce Evidence?
When an auditor asks for the full record of one AI decision, model quality is not enough. Your runtime must show authorization, evidence, oversight, and audit history.
Security & Governance IT Leaders -
AI Agent Pricing: Per-Action Billing vs. Self-Hosted Runtime Cost
At $0.10 per Agentforce action, a successful agent can make usage-based pricing rise quickly. Compare per-action billing with a self-hosted runtime before you scale.
Security & Governance Business Leaders AI agentsAgentforce -
Will Ontologies Become a Standard Part of the AI Stack? Why the Runtime Must Be Open
Will ontologies become a standard part of the AI stack? The agent interface already has: Ontology MCP went GA in June 2026. Definitions are following. The runtime stayed closed, and portability lives there.
Security & Governance Business Leaders OntologyMCPPalantirSemantic layer -
Where AI Agent Permissions Are Enforced: Row-Level Security, Field Masking, and Tool Gates
Everyone agrees an AI agent should respect permissions. The real question is where the check runs. Filtering the model's output is too late — enforcement belongs in the query, the field, and the tool gate.
Security & Governance IT Leaders AI agentsAgent permissions -
Self-Hosted AI Application Platforms: Why the Runtime Belongs to You
Once AI reads business data, triggers workflows, generates applications, and calls tools, enterprises need control over the runtime that governs objects, permissions, tools, approvals, and audit evidence.
Security & Governance IT Leaders -
How AI Agents Stay Inside Enterprise Permission Boundaries
Enterprise teams do not need AI agents to become unrestricted administrators. They need agents that act as controlled users, inherit permissions, route risky actions for approval, and leave an audit trail.
Security & Governance IT Leaders AI agentsAgent permissions